Manual testing by certified pros
OSCP, OSCE, OSWE, OSEP and CRTO-certified testers who think like attackers, not scanners.
Penetration testing · EU-based team
Thanks, your request is in. We usually reply within 1 business day.
Prefer to talk now? Call +40 373 806 832



OSCP, OSCE, OSWE, OSEP and CRTO-certified testers who think like attackers, not scanners.
Every finding comes with proof of concept, business impact and step-by-step fix guidance.
We verify your fixes at no extra cost and issue an updated report and attestation letter.
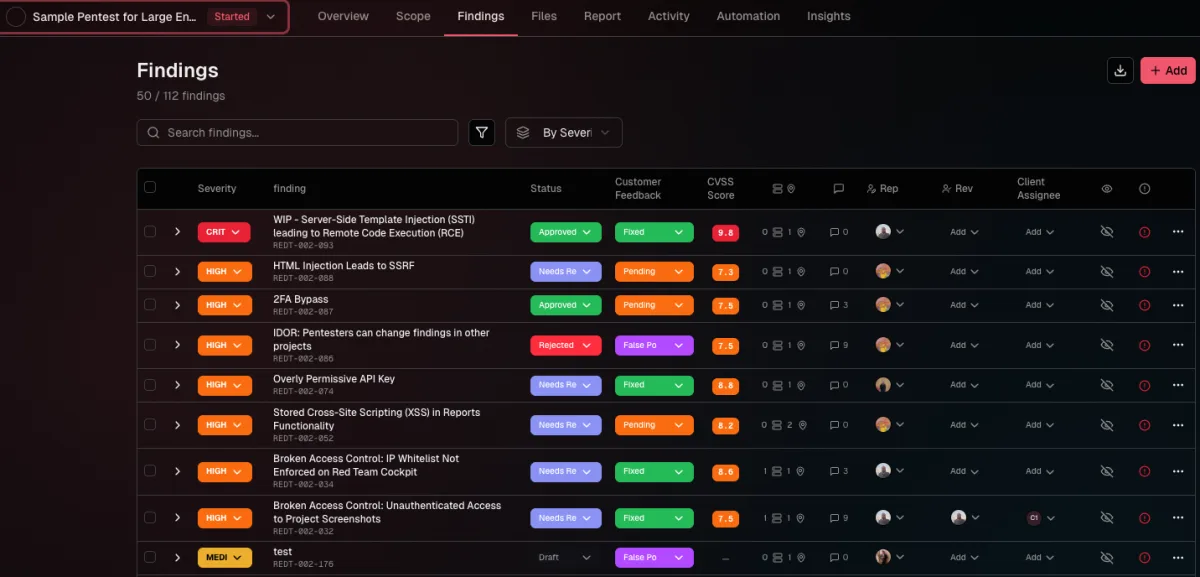
Follow findings as they are discovered in the Red Team Cockpit, our client portal.
Cybersecurity insights that translate across the organization, from technical teams to the boardroom.
Understand exactly where you are vulnerable and what attackers could exploit.
Detailed technical findings with reproduction steps and evidence
Clear risk ratings tied to business impact and financial exposure
Not all vulnerabilities are equal. We rank findings by real-world exploitability and business impact.
CVSS scoring, attack chain analysis and remediation code samples
Resource allocation guidance and risk reduction roadmaps
Satisfy audit requirements and demonstrate due diligence to regulators, customers and partners.
Mappings to OWASP, NIST, CIS and industry frameworks
Audit-ready reports and compliance attestation letters
Track your security posture over time and see how remediation translates to reduced risk.
Vulnerability trending, retest verification and regression tracking
Security scorecards and progress dashboards for leadership
Clear guidance means your team can start fixing issues immediately, not weeks later.
Step-by-step remediation instructions with code examples
Reduced mean time to remediation and shorter exposure windows
Demonstrate security commitment to customers and partners. Win deals where security is the deciding factor.
Technical documentation for customer security questionnaires
Executive summaries suitable for customer and investor communications
From web applications to industrial control systems, we have specialized expertise across your entire technology stack.
Application security
Comprehensive assessment against OWASP Top 10 and advanced attack vectors: authentication, injection, business logic, client-side flaws.
iOS and Android assessment including app internals, local data storage, certificate pinning and backend APIs.
Focused testing of REST, GraphQL, gRPC and microservice architectures: authorization, rate limiting, data exposure.
Multi-tenant assessment for SaaS platforms: tenant isolation, privilege escalation, data leakage, subscription bypass.
Infrastructure security
Perimeter testing of internet-facing systems, services and entry points, including SSL/TLS and DNS.
The insider perspective: segmentation, privilege escalation, lateral movement, Active Directory attacks.
WPA2/WPA3 testing, rogue access points, evil twin and client-side wireless attacks.
Operational technology and industrial control systems: SCADA/DCS, PLCs, protocols, safety systems.
Cloud & modern infrastructure
Configuration review and attack simulation: IAM policies, storage, network security groups, serverless.
Container escape, Kubernetes RBAC, image security, network policies and secrets management.
CI/CD pipeline security, secret detection, dependency analysis and infrastructure as code.
Specialized testing
Prompt injection, model extraction, training data exposure, jailbreaking and API security.
Manual and automated analysis of application source code, architecture and dependencies.
Full adversarial simulation of your people, processes and technology, including detection and response testing.
Kickoff call, asset list, rules of engagement and a fixed-price quote.
Manual testing by certified experts, with findings visible in your portal as we go.
Technical report with PoC, executive summary and a walkthrough with your team.
We verify your fixes and issue the final attestation letter.
Reports accepted for ISO 27001, SOC 2, PCI-DSS, NIS2, DORA, ASF/BNR.
Red Team Cockpit · your client portal
Get real-time visibility into progress, findings and remediation, and collaborate directly with our team in the Red Team Cockpit.
See findings as they are discovered, not weeks later.
Filter, sort and export findings. Assign them to team members.
Chat with the testers, ask questions, request clarifications.
Generate reports on demand in multiple formats.
“We’re already at our third collaboration for penetration testing services, as the team continues to impress us with their professionalism and ethics. Their proactive approach and thorough testing have provided us with invaluable insights into our platform’s security.”
“Whenever we or our clients had a suspicion of data breach or asked for a cybersecurity partner, Bit Sentinel team had a very fast response and always managed to satisfy even the most demanding requirements. I highly recommend Bit Sentinel for penetration testing, code review or any incident response situation.”
“The audit was quick, comprehensive and wrapped up with a detailed report that included all the findings, conclusions, and recommendations from their checks. We’re pleased that their services met our expectations and highly recommend Bit Sentinel for excellent cybersecurity work.”
Most engagements take 2–4 weeks from kickoff to final report. Active testing runs 5–10 business days depending on scope. Urgent timelines can be accommodated.
Testing is designed to minimise disruption. Potentially dangerous tests (such as DoS) are only performed with explicit approval and in agreed maintenance windows. We can pause immediately if needed.
OSCP, OSCE, OSWE, OSEP and CRTO, among others. Bit Sentinel is ISO 27001 certified and Trusted Introducer accredited.
Yes. Every engagement includes a free retest to verify your remediation, followed by an updated report and attestation letter.
Fixed price per engagement, based on scope (applications, endpoints, IP ranges, user roles) and depth. You receive a written quote within 48 hours of scoping, with no hourly surprises.
Send the form or call us. We usually reply within 1 business day.
Call +40 373 806 832